In an era where digital infrastructure serves as the backbone of global commerce, the rise of ransomware has transformed from a nuisance into a systemic threat. No longer the domain of isolated hackers targeting home users, today’s ransomware operations function like sophisticated, multinational criminal corporations. From the manufacturing plants of the German Mittelstand to international logistics conglomerates, entire production lines are being brought to a standstill by unseen adversaries who demand payment in untraceable cryptocurrency.
In this deep dive, we examine the mechanics of these attacks, the critical decision-making processes required during a crisis, and the preventive measures that distinguish resilient organizations from those that collapse under the pressure of a cyber-siege.
The Anatomy of a Modern Ransomware Attack
At its core, a ransomware attack is a digital hostage situation. Criminal syndicates gain unauthorized access to a corporate network—often through phishing, exploiting unpatched software vulnerabilities, or compromised third-party credentials. Once inside, they move laterally, escalating their privileges until they gain control over critical servers and databases.

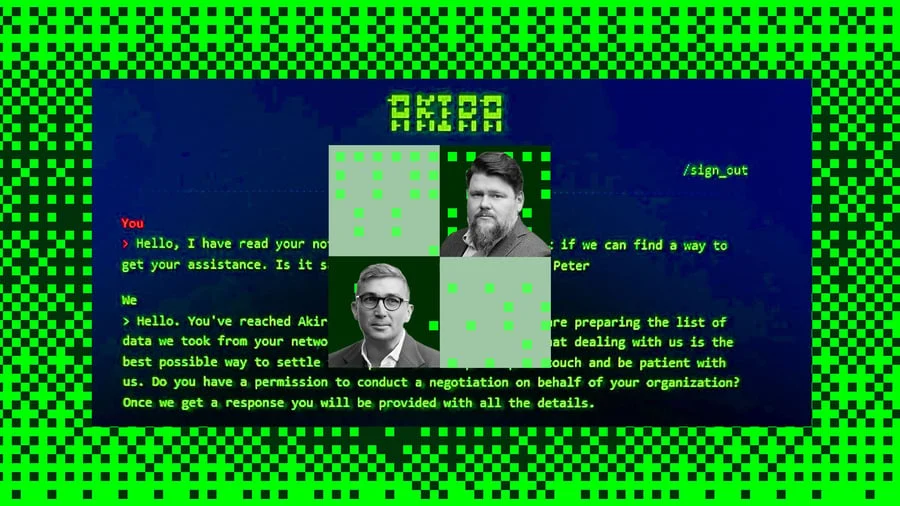
The "payload"—the actual ransomware software—is then deployed. It encrypts mission-critical files, rendering them inaccessible to the company. The attackers then leave a ransom note, typically demanding payment in Bitcoin or Monero in exchange for a decryption key. Increasingly, these criminals employ a "double extortion" tactic: they steal sensitive data before encrypting the systems, threatening to leak trade secrets, employee records, or customer information on the dark web if the ransom is not paid.
The Human Element: Crisis Negotiation
Michael Sjöberg, a former specialist in hostage negotiations for the Danish military, and Peter Skovbo, who directs the Swiss-based crisis firm Delta Crisis, emphasize that cyber-attacks are fundamentally human crises that manifest through technology.
"Cyber-criminality always impacts the entire company, not just the IT department," Sjöberg explains. When a company finds its operations paralyzed, the initial response is often marked by panic and fragmentation. Sjöberg and Skovbo note that the first few hours are the most critical, yet they are often where the most expensive mistakes are made.

Chronology of a Crisis: From Detection to Resolution
To understand the severity of these events, one must look at the timeline of a typical incident response effort.
Phase 1: Detection and Immediate Containment (Hours 0–6)
The alarm is usually triggered by a production halt or an employee reporting an inability to access files. This is the "Golden Window." Successful companies have an Incident Response (IR) plan ready to activate. Immediate containment involves isolating infected segments of the network to prevent the malware from spreading further.
Phase 2: Damage Assessment (Hours 6–48)
IT forensics teams must determine the scope of the encryption. Were backups affected? Is there evidence of data exfiltration? During this time, legal counsel, cyber-insurance providers, and external negotiators like those at Delta Crisis are brought into the loop.
Phase 3: The Decision Point (Days 2–5)
This is where the pressure peaks. "Even the fastest, most effective technical solutions often take at least five days to implement," note the experts at Delta Crisis. Businesses must decide: Can they restore from clean backups? Or is the downtime so catastrophic—potentially leading to permanent market share loss or bankruptcy—that negotiation with the attackers becomes a necessary evil?
Phase 4: Recovery and Forensics
Whether the ransom is paid or not, the recovery process is arduous. Systems must be wiped, rebuilt, and patched. Only then can data be restored. Following this, a comprehensive post-mortem analysis is required to identify the root cause and ensure the vulnerability cannot be exploited again.
Supporting Data: The Rising Cost of Inaction
The financial impact of a ransomware attack extends far beyond the ransom demand itself. Industry reports consistently show that the true cost of an attack includes:

- Business Interruption: The loss of revenue during the period of downtime.
- Forensic and Legal Fees: Retaining cybersecurity firms to investigate the breach and legal counsel to manage regulatory reporting requirements (such as GDPR).
- Reputational Damage: The long-term erosion of client trust and potential devaluation of the brand.
- Remediation Costs: The investment required to overhaul IT infrastructure to prevent future incidents.
According to global cybersecurity metrics, the average total cost of recovery from a ransomware attack has nearly doubled in the last three years, as criminals have become more aggressive in their targeting of mid-sized firms that may lack the robust security budgets of multinational tech giants.
Expert Perspectives: How to Negotiate and Protect
The Negotiation Paradox
Negotiating with criminals is a contentious issue. Law enforcement agencies, including the FBI, generally advise against paying ransoms, as it funds future criminal activities and provides no guarantee that data will be returned or kept confidential. However, for a company facing total collapse, the reality is more nuanced.
Sjöberg and Skovbo emphasize that if a company is forced into the negotiation process, it must be handled by professionals who understand the psychological levers of the attackers. "You are not just dealing with code; you are dealing with a business transaction, albeit an illegal one," they explain. Negotiators work to verify that the attackers actually possess the decryption key and, if possible, to lower the ransom amount.

Strategic Prevention
The best way to handle a ransomware attack is to never be in a position where it is an existential threat. This requires a "Defense-in-Depth" strategy:
- Immutable Backups: Ensure that copies of your data are stored in a format that cannot be altered or deleted by the ransomware. These should be kept offline or in a separate, air-gapped network.
- Zero Trust Architecture: Assume the network is already compromised. Implement strict access controls so that even if a user is breached, the attacker cannot easily move to sensitive areas.
- Regular Tabletop Exercises: A plan is useless if the team hasn’t practiced it. Companies should conduct regular simulations of ransomware scenarios to identify gaps in their communication and response protocols.
- Endpoint Detection and Response (EDR): Deploy advanced security tools that can identify anomalous behavior in real-time and automatically quarantine suspicious processes.
Implications for the Global Economy
The rise of ransomware has fundamentally changed the corporate risk landscape. Insurance premiums for cyber-coverage have skyrocketed, and boardrooms are now being held accountable for their company’s digital hygiene.
Furthermore, the "professionalization" of cyber-crime means that ransomware is now a service industry. "Ransomware-as-a-Service" (RaaS) models allow low-level criminals to purchase sophisticated malware kits, meaning the sheer volume of attacks will continue to increase. For the medium-sized enterprise, this means that security is no longer an "IT issue"—it is a core business risk that demands the same level of oversight as financial reporting or regulatory compliance.

Conclusion: The Path Forward
The warning from experts like Sjöberg and Skovbo is clear: the threat of a cyber-attack is no longer a matter of "if," but "when." The survival of a business in the face of such an event depends entirely on the preparation that occurred long before the first file was encrypted.
By investing in robust, immutable backup systems, fostering a culture of cybersecurity awareness among employees, and maintaining a clear, practiced crisis management strategy, firms can move from a state of vulnerability to one of resilience. While the digital threat landscape will continue to evolve, the fundamental principles of preparation, rapid response, and strategic decision-making remain the most effective tools in the arsenal against digital extortion. The companies that thrive in the coming decade will be those that accept this reality and act decisively to fortify their digital borders.