

Introduction: A New Digital Battlefield
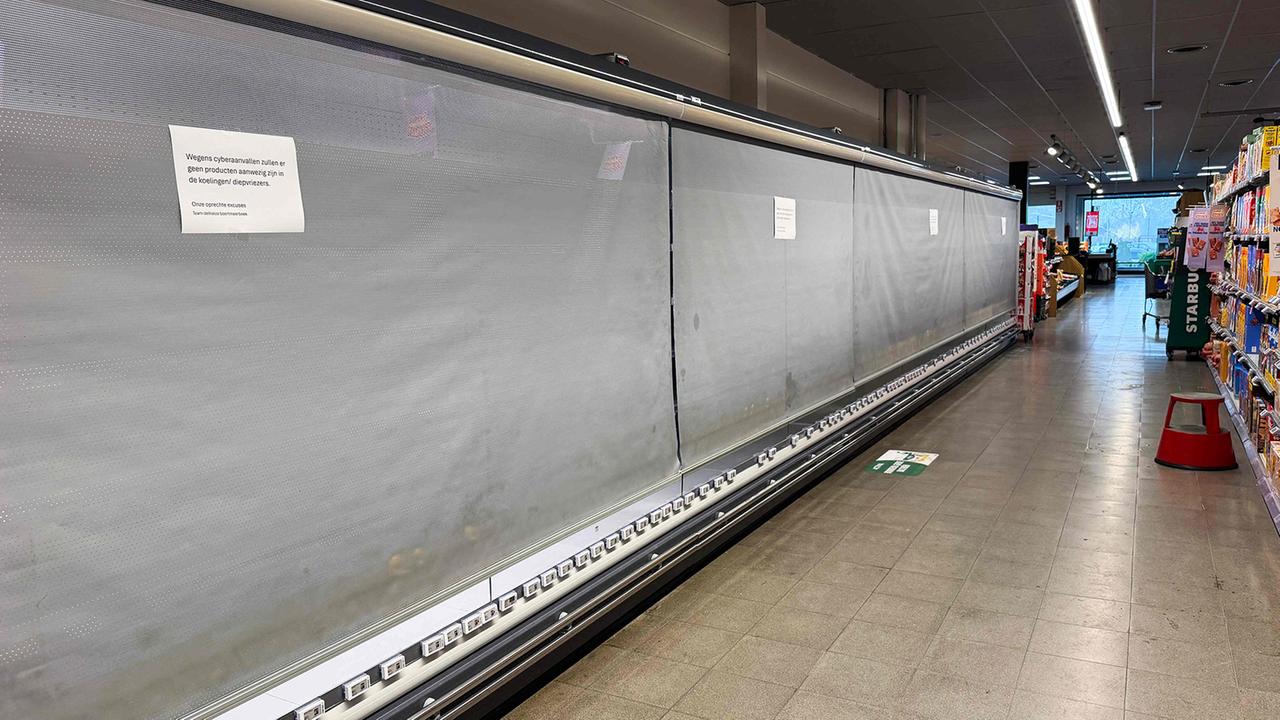
In an era where the “Internet of Things” (IoT) promises unprecedented convenience and efficiency, a stark reality has emerged: our physical infrastructure is only as secure as its weakest digital link. Recent weeks have seen a troubling development in the European retail sector, as a wave of sophisticated cyberattacks targeting supermarket cooling systems has migrated from France to Germany. These incidents have exposed a profound failure in industrial cybersecurity, revealing that major retail chains and equipment manufacturers have, in many cases, left their critical infrastructure effectively defenseless.
The situation is not merely a technical glitch; it is a systemic failure. By connecting sensitive refrigeration management systems directly to the public internet without the protection of firewalls or robust encryption, operators have essentially left the "digital back door" wide open. As experts warn, the implications extend far beyond spoiled food—they threaten the stability of the food supply chain and highlight a dangerous complacency in how we secure the critical infrastructure of modern life.
The Anatomy of the Attacks: A Chronology of Vulnerability
The pattern of these attacks is chillingly consistent. Roughly three weeks ago, a widespread campaign of cyber-intrusions struck cooling arrays in French supermarkets. The ripples of this event quickly crossed the border into Germany, confirming that the threat is not localized but part of a broader, coordinated, or at least opportunistic, targeting of industrial control systems (ICS).
The mechanism is deceptively simple for a sophisticated attacker. Modern supermarket refrigeration units are designed for remote management. They utilize small, integrated web servers that allow facility managers to adjust temperatures, monitor energy usage, and receive diagnostic alerts from a centralized location. However, in the rush to digitize and optimize, the basic tenets of cybersecurity were bypassed.
According to Manuel Atug, a spokesperson for the AG KRITIS (a working group focused on critical infrastructure), many of these systems were installed with a “plug-and-play” mentality. “Supermarkets took these insecure systems—which often contain their own embedded, lightweight web servers—and connected them directly to the internet without any oversight,” Atug explains. “Once that connection is established without a firewall, anyone with the technical know-how to scan the public web for these specific devices can access the controls and manipulate them.”
The Regulatory Lacuna: Defining "Critical"
The security failures in the retail sector raise a critical question: how are these companies regulated? In Germany, legal definitions of "Critical Infrastructure" (KRITIS) are strictly tied to population coverage. Under the current framework, a commercial entity is generally classified as critical infrastructure if it provides essential services to at least 500,000 people.
However, this threshold creates a dangerous middle ground. Even those retailers serving smaller populations fall under the purview of "important" or "particularly important" facilities, which legally obligate them to implement stringent cybersecurity measures. Despite these mandates, the reality on the ground suggests a massive gap between legislative theory and operational practice.
The issue is compounded by the complexity of the supply chain. As Professor Haya Schulmann, Chair of Cybersecurity at the Goethe University Frankfurt, points out, our definition of critical infrastructure is too narrow. “We rely on a vast web of suppliers, contractors, and service providers,” she notes. “If a construction firm or a niche software provider for HVAC systems is compromised, it can delay the repair or maintenance of essential infrastructure. We must broaden our scope to protect the entire supply chain, not just the front-facing entities.”
Systemic Failures: Even the State Is Unprepared
The vulnerability of the private sector is mirrored by equally troubling findings within the public sector. Recent research from the National Research Center for Applied Cybersecurity (ATHENE) suggests that even German federal ministries are failing to meet basic security standards.
The study exposed a landscape of "digital decay":
- Legacy Hardware: The presence of outdated devices that are no longer receiving security patches.
- Unclosed Gaps: Known vulnerabilities remaining unaddressed for extended periods.
- Governance Failures: A lack of standardized requirements for third-party service providers who have privileged access to government networks.
Perhaps most alarming is that these systemic risks are often absent from the official risk assessment reports issued by the Federal Office for Information Security (BSI). “Our investigation showed that even the official situation reports overlook a significant portion of the actual IT footprint of the federal government,” says Professor Schulmann. “You cannot defend what you do not know you have. The agencies responsible for oversight must gain a comprehensive, real-time understanding of the assets they are tasked with protecting.”
The AI Paradox: A Double-Edged Sword
As the threat landscape evolves, the role of Artificial Intelligence (AI) has become the central focus of the debate. On one hand, AI represents a massive force multiplier for cybercriminals. With AI-driven tools, attackers can identify vulnerabilities in firmware or network configurations faster and with less specialized human expertise than ever before. A task that once required a team of skilled hackers can now be automated to scan thousands of systems per hour, identifying those without firewalls with surgical precision.
However, the industry is also banking on AI to be the solution. Research is currently pivoting toward making systems "self-healing" or inherently resilient. The goal is to move beyond the impossible task of preventing every single intrusion and toward building systems that can maintain essential functions even while under attack.
Loui Al Sardy, a cybersecurity researcher at the Friedrich-Alexander-University Erlangen-Nuremberg, offers a sober perspective. “Total, one-hundred-percent security has never existed in the history of computing, and AI will not change that fundamental truth,” he argues. Instead, he advocates for a shift in strategy:
- Reliability: AI systems must remain functional even when fed manipulated or malformed data by attackers.
- Explainability: Security decisions made by AI models must be transparent enough for human auditors to understand.
- Risk Awareness: Operators must recognize the limits of AI, acknowledging its propensity for generating false positives or missing sophisticated, "low-and-slow" attacks.
- Human Oversight: Security, privacy, and the human element must remain the final arbiter of system control.
Implications: The Path Forward
The recent cyberattacks on supermarket cooling systems serve as a wake-up call for the entire industrial sector. The "convenience-first" approach to networking has created a massive, distributed vulnerability that adversaries are now exploiting with alarming regularity.
For the retail industry, the solution is immediate and non-negotiable: every device connected to the internet must be shielded by a robust, enterprise-grade firewall. Beyond this, the industry must embrace a "Zero Trust" architecture, where internal systems do not automatically trust incoming traffic, even if it originates from within the network.
For policymakers, the message is equally clear: the definition of critical infrastructure must be dynamic. The dependency of the population on food, water, and electricity is absolute, and the digital systems that underpin these services are now as essential as the physical hardware itself.
The era of ignoring cybersecurity in industrial management is over. As we integrate more intelligence into our infrastructure, we must match that progress with a corresponding evolution in our defensive posture. The security of the nation’s supply chain depends not on the sophistication of the latest AI tool, but on the disciplined, rigorous application of fundamental security practices that have been ignored for far too long.
The cold truth is that while the hackers are evolving, our basic defenses have been left in the deep freeze. It is time to thaw out the stagnant security policies of the past and secure the digital infrastructure that keeps our society running.