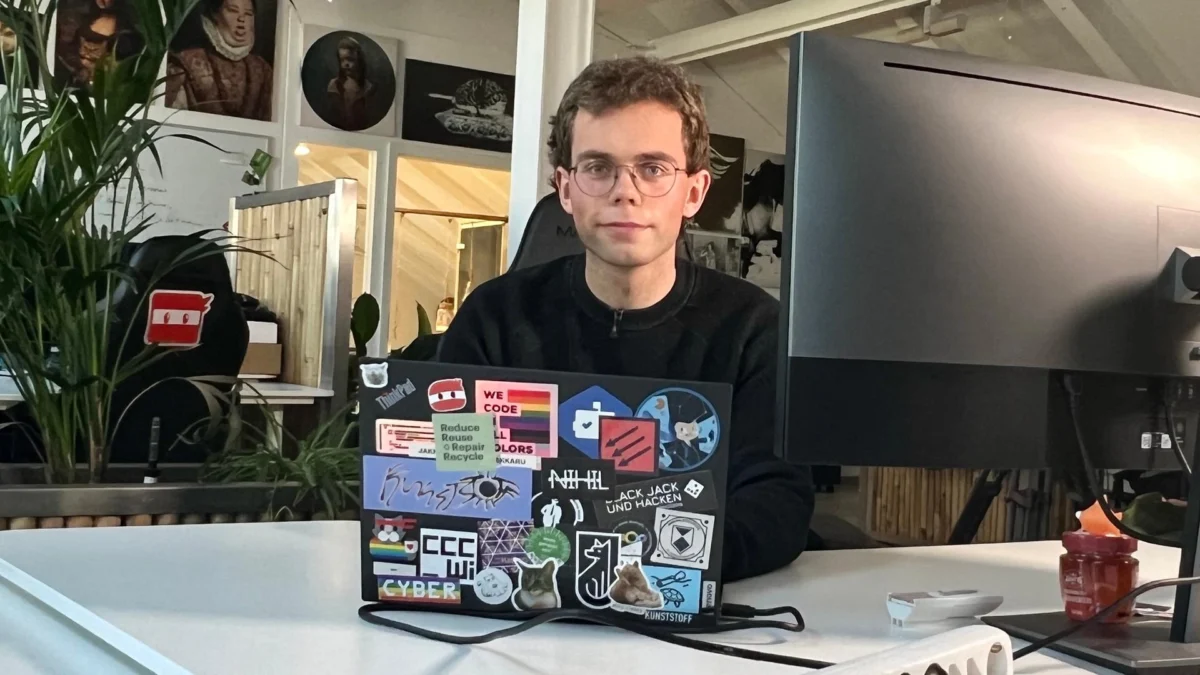
In mid-August, Marlon Starkloff, a 23-year-old software developer and ethical hacker from Kassel, Germany, sat before his computer and gained access to a digital control center that could have theoretically plunged Europe into darkness. With just a few clicks, Starkloff bypassed the security layers of the Chinese electronics giant Sungrow, effectively granting himself administrative control over hundreds of thousands of solar energy systems across Europe.
This wasn’t a malicious breach intended to sabotage the power grid, but a calculated discovery by a security professional. The vulnerability he uncovered highlights a systemic risk in the global transition to renewable energy: as we decentralize our power generation through millions of residential solar arrays, we are simultaneously creating a massive, interconnected attack surface that is often protected by inadequate cybersecurity infrastructure.
A Chronology of Discovery: The Week That Could Have Changed Everything
The path to uncovering the vulnerability was neither accidental nor instantaneous. Starkloff, the managing director of the security firm Jakkaru, spent an entire week systematically probing the Sungrow cloud ecosystem. His primary tool was not just raw coding skill, but the strategic application of Artificial Intelligence (AI) to identify patterns and weaknesses in the company’s web architecture.
Starkloff began by creating a standard user account on the Sungrow cloud platform—the same portal used by homeowners to monitor their residential photovoltaic (PV) inverters. However, his curiosity led him to examine the underlying structure of the login process. He discovered that the system utilized eight different login types, each with varying levels of privilege. Through persistent testing, he identified one specific administrative login type that lacked a password requirement.
By exploiting this bypass, Starkloff gained high-level administrative access. He was suddenly presented with a dashboard displaying the sensitive data of approximately 470,000 systems, 250,000 of which were located within Germany. The data included precise locations—down to the street and house number—of individual households, as well as operational data for the inverters themselves.
The Magnitude of the Threat: From Data Leak to Blackout
The implications of this breach extend far beyond a simple privacy violation. According to Starkloff, the potential for harm was global, affecting an estimated 2.5 million devices worldwide. Had this vulnerability fallen into the hands of a malicious state actor or a sophisticated cyber-criminal organization, the results could have been catastrophic.
Starkloff demonstrated that a hacker with such access could, in theory, deploy malware to every connected inverter simultaneously. If an attacker were to issue a command for these devices to shut down at high noon on a sunny summer day, the impact on the European power grid would be instantaneous.
"We are talking about 17 gigawatts of power being pulled from the grid in a single moment," Starkloff explained during an interview. "It is highly doubtful that the European interconnected grid would have been able to absorb such a shock. The result would likely have been a cascading failure—a blackout."

The Manufacturer’s Response: A Tense Disagreement
Following the discovery, the situation escalated into a public debate between the researcher and the manufacturer. Sungrow acknowledged the existence of the security flaw but moved to minimize the potential impact reported by Starkloff.
In an official statement, a company spokesperson admitted that a "faulty login module" had indeed allowed unauthorized parties to bypass standard authentication processes. However, Sungrow maintained that the secondary, critical layers of security—specifically the password-protected settings required to change the core parameters of the inverters—remained intact. The manufacturer argued that while the accounts were visible, the ability to remotely disable them was not possible through the exploited module alone.
Furthermore, Sungrow was unable to provide an exact count of the affected systems. The company noted that their platform does not track every solar installation globally, as many users opt out of cloud registration or use third-party monitoring software.
Ethical Hacking: The "Cat-and-Mouse" Game of Modern Security
For Marlon Starkloff, this high-stakes investigation is all in a day’s work. As an ethical hacker, his profession involves identifying vulnerabilities before those with malicious intent can find them. He has previously conducted security audits for the European Space Agency (ESA), the solar firm Fox Ess, and regional German economic development agencies.
Starkloff notes that the rise of AI has significantly lowered the barrier to entry for both defensive and offensive cybersecurity. "It’s a constant game of cat-and-mouse," he notes. "The attackers are often one step ahead, and when they aren’t the ‘good guys,’ companies face devastating consequences."
His efforts were rewarded with an 800-euro "bug bounty"—a modest payout for a discovery that effectively saved a massive portion of the energy infrastructure from potential catastrophe.
Regulatory and Systemic Implications
The incident caught the attention of the Federal Office for Information Security (BSI) in Germany. Upon receiving the report, the BSI coordinated with Sungrow to deploy a "hotfix," closing the security hole immediately. Fortunately, the BSI confirmed there was no evidence that the vulnerability had been exploited by any third party prior to Starkloff’s discovery.
However, the BSI used the event as a wake-up call for the entire renewable energy sector. A spokesperson for the agency emphasized that the concentration of power control within cloud platforms is a structural risk. When hundreds of thousands of individual energy producers are managed through a single, centralized cloud portal, that portal becomes a "single point of failure."

The BSI’s recommendations are clear:
- Strengthen Security Standards: Inverters and energy storage systems must undergo more rigorous security testing before they reach the market.
- Prioritize Domestic/Trusted Providers: The BSI advises the use of equipment from manufacturers who are subject to European jurisdiction, ensuring that security lapses can be addressed through legal and regulatory channels.
- Smart-Meter Security: While the industry pushes for "smart" connectivity, the BSI notes that true system stability must rely on secure gateways, not just convenient cloud apps.
The Dilemma of Connectivity: Practicality vs. Security
The suggestion by some experts to simply disconnect solar inverters from the internet is met with skepticism by energy informatics experts like Manuel Wickert of the Fraunhofer Institute.
"For the user, the internet connection is a major benefit," Wickert explains. "It allows for remote monitoring and, more importantly, allows manufacturers to push essential security patches to hardware in the field."
The conflict lies in the nature of modern energy management. To balance the grid, network operators need to be able to communicate with distributed energy sources. This necessity creates a "digital bridge" that can be crossed by attackers. Wickert warns that the scale of the threat is immense, pointing to the 2025 power outages in Spain and Portugal as a cautionary tale of what happens when critical infrastructure fails on a massive scale.
Conclusion: A Call for Hardened Infrastructure
The Sungrow incident is a microcosm of the risks inherent in the digital transformation of the energy sector. As we move toward a carbon-neutral future, we are shifting from a few large, highly secure power plants to millions of small, internet-connected devices.
If this transition is to succeed, the industry must shift its focus from "feature-rich" connectivity to "security-first" design. For homeowners, the takeaway is a sobering reminder that their smart-home energy systems are part of a much larger, and potentially fragile, European ecosystem. While Starkloff’s discovery prevented a potential crisis, it serves as a stark warning: in the age of the digital grid, cybersecurity is no longer an IT issue—it is a matter of national and continental security.