By Industry Analysis Desk
The landscape of digital security is currently undergoing a period of intense scrutiny following a series of high-profile vulnerabilities, most notably within the widely used programming language, PHP. As businesses grapple with the rising tide of cyber threats, many have turned their attention to the role of Artificial Intelligence (AI) as the new frontier of offensive and defensive warfare. However, according to leading cybersecurity experts, the reality of the threat landscape is more nuanced—and perhaps more dangerous—than the buzz surrounding AI suggests.
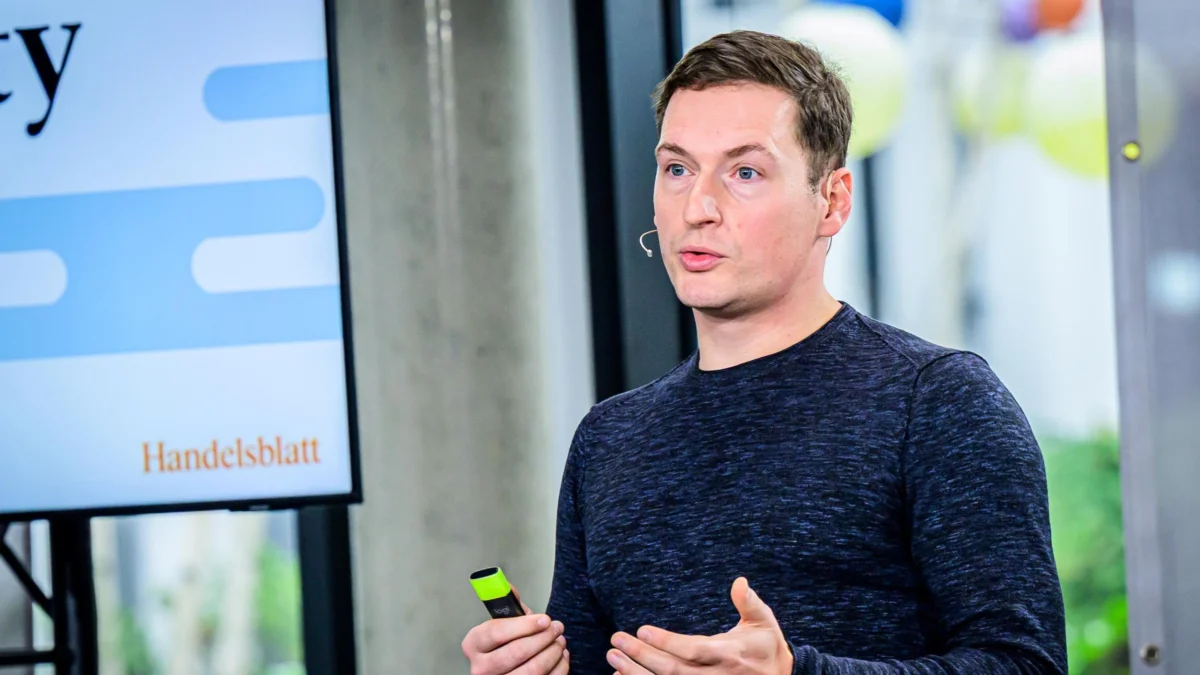
Sven Herpig, Head of Cybersecurity at Interface, argues that while the integration of AI into malicious workflows is a genuine development, it is not the primary driver of current instability. In an exclusive discussion regarding the recent PHP security crises, Herpig posits that the fundamental weakness of global digital infrastructure has been present for decades, and AI is merely accelerating an already established trajectory of exploitation.
The Core Facts: A Persistent Vulnerability
At the heart of the current debate is the structural integrity of the software supply chain. PHP, which powers a massive portion of the world’s websites, recently faced critical security disclosures that left thousands of servers exposed to remote code execution (RCE) attacks.
The mechanism of attack is a classic yet potent cycle:
- The Disclosure: A vulnerability is discovered in the core code of a widely used software platform.
- The Patch: Developers release a security update (patch) to close the hole.
- The Reverse Engineering: Malicious actors immediately deconstruct the patch to understand the specific mechanism of the flaw.
- The Race: Attackers attempt to compromise systems that have not yet installed the update, while defenders scramble to apply fixes.
This "cat-and-mouse" game is not new. What has changed, however, is the speed at which this cycle operates. What once took weeks for a sophisticated threat actor to exploit—the time required to reverse engineer a patch and weaponize it—has been compressed into days, or in some cases, mere hours.

Chronology of an Escalating Threat
To understand the current state of cybersecurity, one must look at the timeline of exploitation maturity:
- The Pre-Automated Era (1990s–2010): Exploitation was largely manual. Attackers relied on human intuition to discover zero-day vulnerabilities and manually craft exploits. The lag between patch release and widespread exploitation was significant.
- The Proliferation of Scripting (2010–2018): Automated vulnerability scanners became accessible. Attackers began using automated scripts to "spray and pray" across the internet, looking for unpatched systems.
- The Era of Advanced Persistent Threats (2018–2022): State-sponsored actors refined the process of "N-day" exploitation—taking a patch that had been released but not yet widely adopted and weaponizing it before the target could remediate.
- The AI Acceleration (2023–Present): The current era sees the application of Large Language Models (LLMs) and machine learning tools to automate the analysis of source code. While the method remains the same—finding a bug, crafting an exploit—the efficiency has reached a breaking point.
Supporting Data: Why "The Internet is Not Going Under"
Despite the alarmist headlines, cybersecurity experts remain cautiously optimistic. The core infrastructure of the internet is resilient, and the "death of the web" is a hyperbole that obscures the real, manageable challenges at hand.
Data from recent security audits suggests that over 70% of successful breaches are still caused by "low-hanging fruit"—basic configuration errors, weak credentials, and delayed patch management—rather than sophisticated, AI-driven zero-day attacks.
The Economics of IT Incidents
A security incident is, above all else, a financial catastrophe. The cost of a breach is not limited to the ransom paid to hackers. It includes:
- Operational Downtime: The cost of being unable to process transactions.
- Reputational Damage: The loss of consumer trust which, for a digital-first company, can be fatal.
- Legal and Regulatory Fines: Increasing scrutiny under frameworks like GDPR or the EU’s NIS2 Directive.
- Remediation Costs: The expense of forensic investigators, legal counsel, and public relations firms.
"An IT incident costs a significant amount of money," notes Herpig. "The business impact is often the most overlooked aspect of cybersecurity, yet it is the primary driver for why companies must prioritize resilience over merely ‘checking boxes’ for compliance."
The Role of AI in Offensive and Defensive Operations
The conversation around AI in security often centers on "deepfakes" or automated phishing, but the real threat lies in vulnerability research.

Offensive AI:
AI models are now being used to parse millions of lines of open-source code to identify potential security flaws before the developers themselves find them. This gives an attacker a massive head start. They do not need to be geniuses; they simply need to be the first to query the model with the right parameters.
Defensive AI:
On the flip side, defenders are utilizing AI to monitor network traffic for anomalies in real-time. Where a human analyst might take hours to sift through logs, an AI agent can detect a lateral movement within a network in milliseconds. The battle, therefore, is becoming a war of algorithms, where the side with the faster, more accurate model gains the upper hand.
Implications: The Necessity of a New Strategy
Given that the "cat-and-mouse" game is accelerating, organizations must shift their strategy from a reactive posture to a proactive one.

1. Shift-Left Security
Security cannot be an afterthought in the software development lifecycle (SDLC). It must be integrated into the coding process itself. By using static application security testing (SAST) tools that are powered by AI, developers can catch vulnerabilities during the coding phase, long before the software is deployed to production.
2. Zero-Trust Architecture
The assumption that a network is "safe" once a user is logged in is outdated. A Zero-Trust model assumes that the network is already compromised. Every request—whether internal or external—must be verified. This limits the "blast radius" if a vulnerability like the PHP flaw is exploited.
3. Rapid Patching Cadence
The data is clear: the window of opportunity for attackers is closing. Organizations that cannot patch their critical systems within 24 to 48 hours of a patch release are significantly more likely to face a catastrophic incident. Automation of the patching process is no longer optional; it is a business requirement.

Official Responses and Regulatory Outlook
Governments worldwide are beginning to recognize that cybersecurity is a matter of national security. The EU, for instance, has introduced the Cyber Resilience Act, which aims to impose stricter security requirements on hardware and software products.
The policy shift is moving toward accountability. Vendors who release insecure software may soon face legal liabilities that were previously shielded by "as-is" licensing agreements. This change in the legal landscape will likely force the industry to prioritize security over the speed of feature releases.
Conclusion: A New Equilibrium
As we look to the future, it is clear that the integration of AI will not bring about the collapse of the internet, but it will force a reckoning within the IT industry. The "old ways" of managing security—relying on manual updates and perimeter-based defenses—are insufficient.
The vulnerability of systems like PHP serves as a reminder that we are building our digital world on a foundation that requires constant, vigilant maintenance. The emergence of AI in this context acts as a mirror, reflecting our own lack of preparedness back at us.
"We don’t need to fear the AI," says Herpig. "We need to fear our own complacency. The tools have changed, the speed has changed, but the fundamental responsibility of the engineer remains the same: to build systems that are secure by design, and to remain faster than the adversary."
In the end, the solution to the AI security paradox is not found in a new piece of software, but in a shift in organizational culture—one that treats every security patch not as a nuisance, but as a critical mission to protect the digital lifeblood of the modern economy.