In an era where data is the lifeblood of global commerce, the specter of ransomware has evolved from a nuisance into a systemic threat. Cybercriminals no longer simply lock files; they exfiltrate sensitive corporate information, cripple critical infrastructure, and hold the continuity of entire organizations hostage. As these attacks increasingly target the "Mittelstand"—the backbone of the economy—the question for business leaders is no longer if an attack will occur, but how they will respond when the screen goes dark.
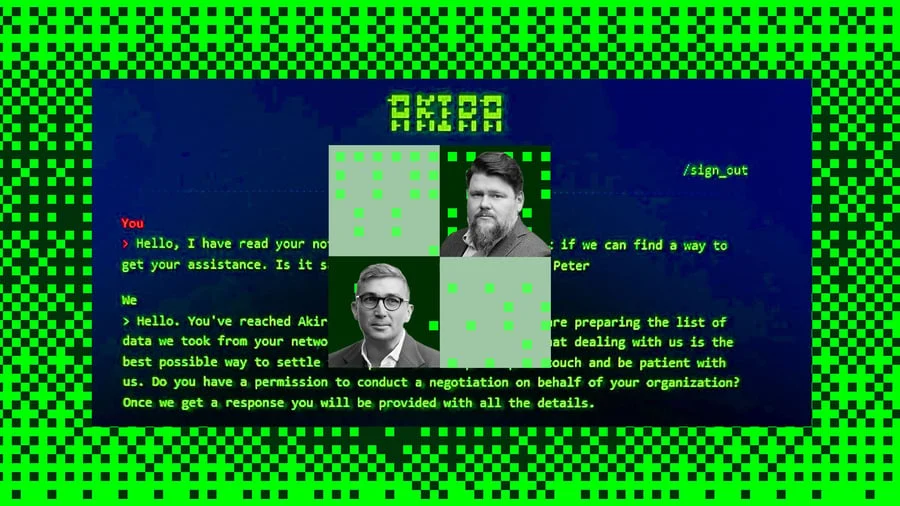
In this comprehensive examination, we delve into the mechanics of ransomware, the critical errors made during the initial hours of a breach, and the strategic imperatives for survival. Drawing on the insights of crisis management experts Michael Sjölberg and Peter Skovbo, founders of the advisory firm Delta Crisis, we outline how firms can navigate the delicate balance between security, legality, and business survival.
The Anatomy of an Attack: Main Facts
Ransomware is a sophisticated form of malware that encrypts a victim’s files, rendering them inaccessible. The attackers then demand a ransom—typically in untraceable cryptocurrency such as Bitcoin—in exchange for a decryption key. However, the modern ransomware landscape has shifted toward "double extortion."

- Encryption: Attackers infiltrate the network, escalate privileges, and encrypt critical databases and production systems.
- Exfiltration: Before the encryption occurs, criminals steal proprietary data, client records, and intellectual property.
- Extortion: The attackers threaten to leak the stolen data on the "dark web" unless the ransom is paid. This forces companies to pay even if they have backups to restore their systems.
The impact is often immediate and catastrophic. Production lines grind to a halt, supply chains are severed, and the reputational damage can be as costly as the financial loss.
Chronology of a Crisis: The First 24 Hours
For most organizations, the first hours of a ransomware incident are defined by chaos. According to Sjölberg, a former Danish military officer specialized in hostage negotiations, the way a company reacts in the first six hours dictates the outcome of the crisis.
Phase 1: The Discovery (Hour 0–2)
Typically, the incident is discovered when employees report that files are inaccessible or systems are unresponsive. The common, and often fatal, mistake is a lack of a pre-existing Incident Response Plan (IRP). Without a plan, IT departments often panic, potentially deleting evidence or inadvertently alerting the attackers that they are being monitored.

Phase 2: Containment (Hour 2–6)
This is the "Golden Window." Technical teams must isolate the infected segments of the network to prevent the spread of the ransomware. However, this must be done strategically. Prematurely shutting down all systems can destroy forensic evidence needed for later investigation and recovery.
Phase 3: Communication and Command (Hour 6–12)
Establishing a "Crisis Management Team" is essential. This group should include C-suite executives, legal counsel, IT security, and external crisis negotiators. It is during this phase that the company must decide how to communicate with the extortionists—if at all—and how to manage external stakeholders, including law enforcement and insurance providers.
Supporting Data: The Rising Tide of Cyber-Extortion
The rise of ransomware is not merely anecdotal; it is supported by stark industry data. Recent reports indicate that the average downtime following a ransomware attack has increased significantly, often lasting between 15 to 22 days. For a medium-sized manufacturing firm, this translates to millions of dollars in lost revenue.
Furthermore, the "success rate" of extortionists is alarming. Statistics show that a large percentage of companies that pay the ransom do eventually recover their data, but there is no guarantee. Moreover, paying the ransom does not prevent future attacks; in many cases, it marks the company as a "willing payer," leading to repeat targeting by other criminal syndicates.
The shift toward the Mittelstand is a strategic move by threat actors. These firms often have robust digital operations but lack the sophisticated security budgets of multinational corporations, making them "low-hanging fruit" with enough liquidity to pay significant ransoms.
The Negotiator’s Perspective: To Pay or Not to Pay?
Peter Skovbo, who directs the operations of Delta Crisis in Switzerland, emphasizes that the decision to negotiate is rarely binary. "Cybercrime always affects the entire enterprise," says Skovbo. "It is not just an IT problem; it is a business continuity problem."

When asked what is typically already wrong when a firm calls for help, the answer is usually: a lack of preparation. Many companies treat cybersecurity as a technical checkbox rather than a business risk management issue.
The Negotiator’s Checklist:
- Avoid Emotional Reactions: Attackers use urgency and fear to force payment. Negotiators act as a buffer, slowing down the process to give the victim time to assess their options.
- The "Proof of Life": Never pay a ransom without receiving a sample decryption to ensure the criminals actually possess the functional tools to restore your systems.
- Regulatory Compliance: In many jurisdictions, paying a ransom to sanctioned groups or individuals can lead to severe legal penalties. Legal counsel must verify that a payment does not violate international anti-money laundering or anti-terrorism laws.
Official Responses and Legal Implications
Governments worldwide are grappling with the legalities of ransomware payments. Some regulators strongly advise against payment, arguing that it funds further criminal activity and perpetuates the cycle. Others recognize that for some businesses, payment is the only path to survival.
The Role of Law Enforcement
Organizations should involve law enforcement (such as the FBI, Europol, or local cybercrime units) as early as possible. While they may not be able to decrypt the files, they provide critical threat intelligence and may have access to existing decryption keys from previous busts of criminal infrastructure.

The Insurance Conundrum
Cyber-insurance has become a double-edged sword. While it provides financial cover for ransom payments and business interruption, insurers are increasingly tightening their requirements. Policies now often mandate strict security protocols, such as Multi-Factor Authentication (MFA) and immutable backups. Failure to adhere to these can result in a denial of claims.
Strategic Implications: Building Resilience
Moving forward, the focus must shift from reactive crisis management to proactive cyber-resilience. This involves several key pillars:
1. The Immutable Backup Strategy
The most effective defense against ransomware is the "3-2-1" rule: three copies of data, on two different media, with one copy stored offline or in an immutable cloud environment. If your backups are connected to the network, the attackers will encrypt them too.

2. Zero-Trust Architecture
Assume the network is already compromised. By implementing a Zero-Trust framework, companies limit the "blast radius" of an attack. If a single employee’s credentials are stolen, the attacker should not have unrestricted access to the entire server infrastructure.
3. Crisis Simulation
Just as fire drills are standard in physical workplaces, "Cyber Drills" should be routine. Testing the leadership team’s response to a simulated ransomware attack helps identify gaps in communication and decision-making long before a real crisis hits.
4. Cultivating a Culture of Vigilance
The majority of ransomware attacks begin with a simple phishing email. Regular training and a culture where employees feel safe reporting suspicious activity are the first and most effective lines of defense.
Conclusion
The digital landscape is inherently hostile, and ransomware represents one of its most persistent dangers. However, the fate of an organization is not determined by the attack itself, but by the robustness of its defenses and the maturity of its crisis response.
As Michael Sjölberg and Peter Skovbo suggest, the goal is to move from a position of vulnerability to one of resilience. By treating cyber-risk as a core business function—integrating it into legal, operational, and executive strategies—companies can ensure that even if they are targeted, they are not defeated. In the final analysis, the most effective tool in the fight against ransomware is not the latest software, but the preparation, discipline, and calm judgment of the people tasked with protecting the enterprise.