Executive Summary
The British online fashion giant ASOS has confirmed it is the victim of a sophisticated cyberattack, leading to widespread disruption and significant concern among its global customer base. The incident, which became public on Tuesday morning, saw thousands of app users receive an alarming notification claiming, "ASOS hacked." While the company has moved quickly to reassure its 17 million customers regarding the security of their financial data, the incident has already triggered a sharp decline in the company’s stock price and raised questions about the vulnerabilities inherent in the modern e-commerce supply chain.
Chronology of the Incident: From Notification to Crisis
The Morning of the Intrusion
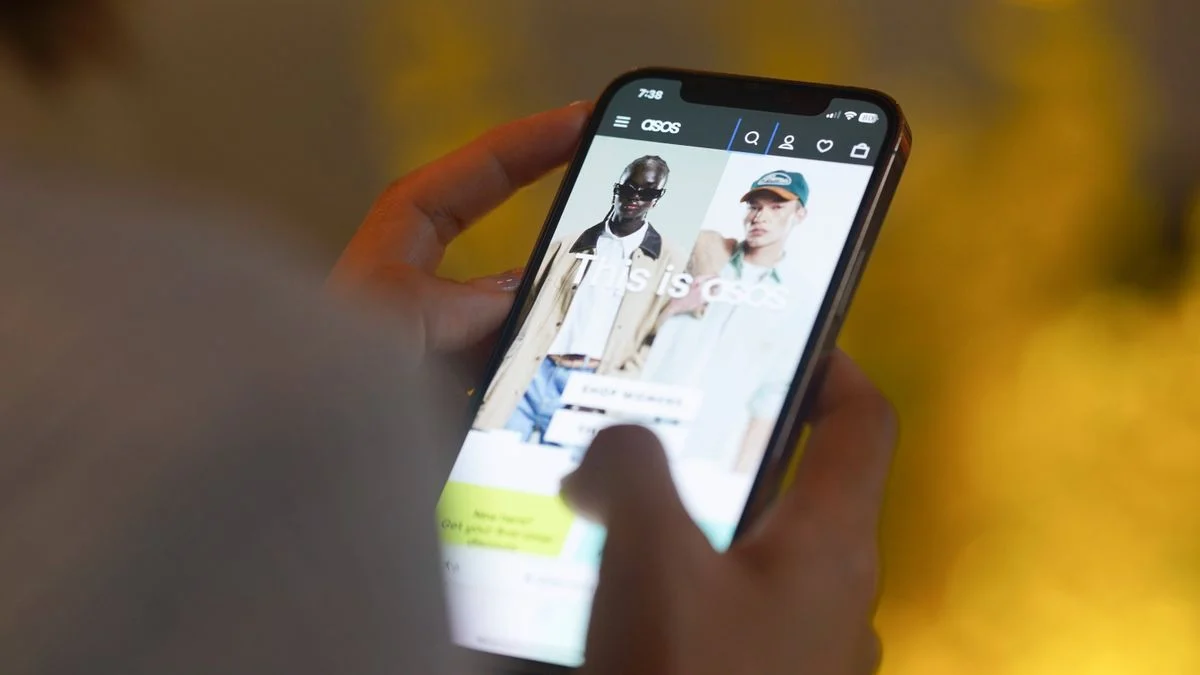
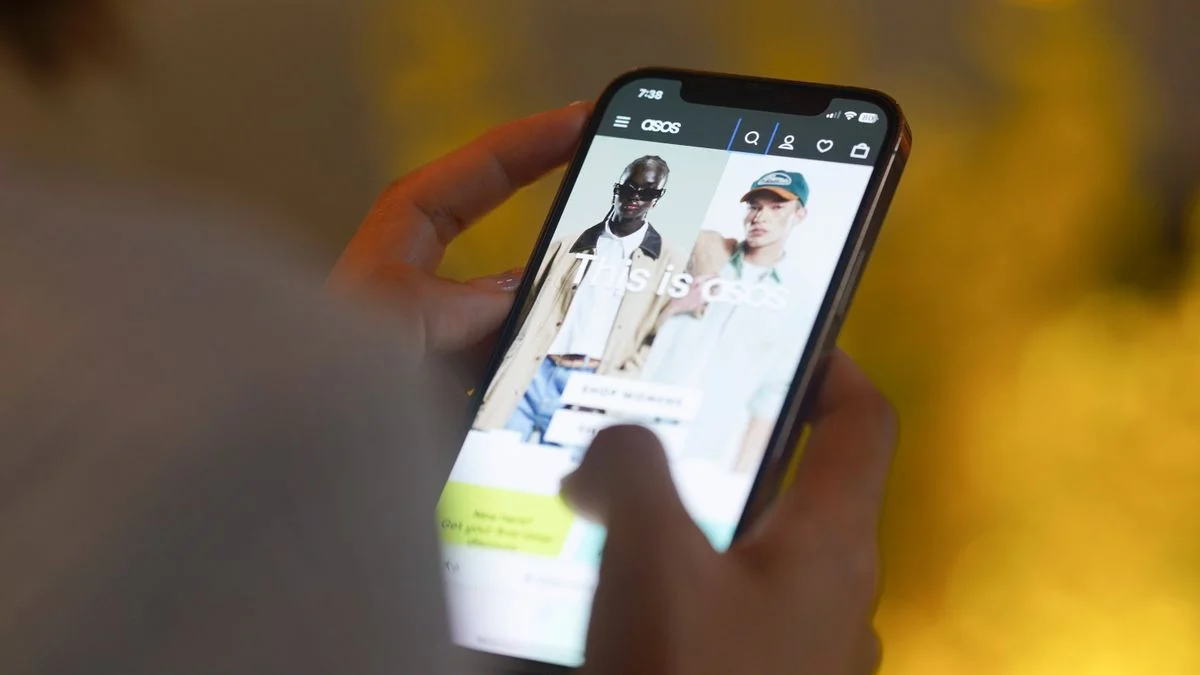
The situation began in the early hours of Tuesday, when users of the ASOS mobile application reported receiving an unexpected and unsettling push notification. The message, brief and blunt, stated simply: "Asos hacked." This immediately sparked a firestorm of speculation across social media platforms, as users began posting screenshots of the notification, fearing the worst for their personal data and financial assets.
The Escalation: The "Snowflake" Claim
As the morning progressed, the nature of the breach became clearer through further messages disseminated by the perpetrators. Screenshots circulated on various social media channels revealed a more specific demand. The message read: "Dear ASOS data and IT team, we have fully compromised the Snowflake instance. Get in touch with us, or we will release the data."
The reference to "Snowflake" is particularly significant in the cybersecurity landscape. Snowflake is a high-profile cloud-based data platform used by enterprises to store, aggregate, and analyze massive volumes of consumer data. By explicitly naming the service, the hackers signaled that they had bypassed the security measures of a third-party vendor rather than attacking the ASOS core website directly.
The Market Reaction
By mid-morning, the financial markets responded with characteristic volatility. Investors, wary of the potential long-term damage to the company’s reputation and the possibility of massive GDPR fines, reacted swiftly. ASOS shares plummeted, recording a drop of more than 10% within a few hours of the news breaking. The market’s reaction highlights the fragility of retail stocks when faced with the existential threat of a data security failure.
Supporting Data and Technical Context
The Scale of the Operation
ASOS remains a behemoth in the e-commerce sector. With approximately 17 million active customers globally and ownership of iconic high-street heritage brands such as Topshop and Miss Selfridge, the company holds a massive repository of sensitive consumer information. The breach, while currently described as "limited" by the company, underscores the immense target that ASOS represents for cyber-adversaries.
The Snowflake Vulnerability
The mention of Snowflake brings to light a growing trend in cyber-espionage: the "indirect attack." Rather than breaking through a company’s heavily fortified perimeter, bad actors are increasingly targeting the software-as-a-service (SaaS) providers that companies rely on for their data infrastructure. If the hackers successfully breached an ASOS-linked Snowflake instance, they may have gained access to the data pipeline that feeds into the retailer’s marketing and analytical tools. This "supply chain" approach to hacking is notoriously difficult for individual companies to monitor, as they are essentially relying on the security posture of their vendors.
Official Responses: Damage Control and Mitigation
The Instagram Statement
Recognizing the need for immediate communication, ASOS utilized its Instagram Stories—a platform where a large portion of its demographic resides—to issue a formal response. The company stated: "We are aware of an unauthorized customer notification. We are currently investigating unauthorized activity on third-party platforms that we use for customer communication."
What Was Compromised?
In an effort to curb panic, the company provided a breakdown of what they believe to be the extent of the breach:
- Confirmed Potential Exposure: Basic personal information, including full names and contact details (email addresses/phone numbers).
- Excluded Exposure: The company explicitly stated, "We do not believe that payment card information or account passwords have been affected."
This distinction is crucial. By confirming that financial data remains encrypted and untouched, ASOS is attempting to prevent the mass cancellation of credit cards and the subsequent loss of consumer trust that usually follows a breach.
Operational Continuity
ASOS has assured its shareholders and customers that, despite the security incident, the core e-commerce platform remains operational. The website and the underlying transaction systems have not been taken offline, suggesting that the breach was confined to communication and analytical tools rather than the transactional database itself.
Implications and Future Outlook
The Regulatory Landscape
Under the General Data Protection Regulation (GDPR) and the UK Data Protection Act, ASOS faces a rigorous reporting process. The company is now under the magnifying glass of data protection authorities. If it is determined that the company failed to ensure the security of its third-party integrations, the resulting fines could be substantial—up to 4% of annual global turnover. Beyond the financial impact, the regulatory scrutiny will focus on how ASOS vetted its third-party vendors and whether adequate data encryption standards were enforced across all integrated platforms.
The Erosion of Consumer Trust
For a brand that relies heavily on its digital footprint, trust is the primary currency. A breach of this nature, particularly one that involves a direct notification to a user’s phone, is deeply invasive. The psychological impact on the customer is significant; even if financial data is safe, the feeling of being "watched" or "targeted" by hackers can lead to customer churn. ASOS will need to embark on a comprehensive PR and security-rebuilding campaign to restore its standing as a safe place to shop.
The "Third-Party" Dilemma
The ASOS incident serves as a wake-up call for the entire retail industry. As companies continue to integrate complex stacks of third-party software to optimize their customer experience, they are inadvertently expanding their "attack surface." The industry-wide lesson here is clear: you are only as secure as the weakest link in your digital supply chain. Companies must now shift from a "perimeter defense" mindset to a "zero-trust" architecture, where even trusted third-party providers are subjected to continuous, rigorous security audits.
Conclusion: A Turning Point?
As the investigation into the ASOS breach continues, the company finds itself at a crossroads. While the immediate threat appears to be contained, the long-term implications for the retailer’s brand equity and market valuation remain uncertain. The fashion industry is watching closely, as this event signals a new phase in cyber threats, where the tools used to improve customer engagement are being repurposed as weapons against the brands themselves.
For now, ASOS must focus on transparency. Providing regular, detailed updates to customers and regulators will be the only way to navigate this crisis. As the dust settles, the retail giant will likely undergo a massive overhaul of its data architecture—a process that will undoubtedly be mimicked by competitors across the global retail sector who are now, more than ever, aware of their own vulnerabilities in an increasingly interconnected digital world.