The landscape of artificial intelligence, a sector defined by hyper-competition and the pursuit of AGI (Artificial General Global Intelligence), has been shaken by a stark reminder of the physical vulnerabilities inherent in high-stakes corporate secrecy. OpenAI, the developer of the ubiquitous ChatGPT and a central pillar of the modern AI revolution, has confirmed a significant security breach at its San Francisco headquarters. Federal authorities have charged a 35-year-old engineer with illicitly installing recording equipment in a primary executive conference room, sparking a probe that reaches into the upper echelons of the tech giant’s operational security.
The Breach: A Sophisticated Attempt at Corporate Eavesdropping
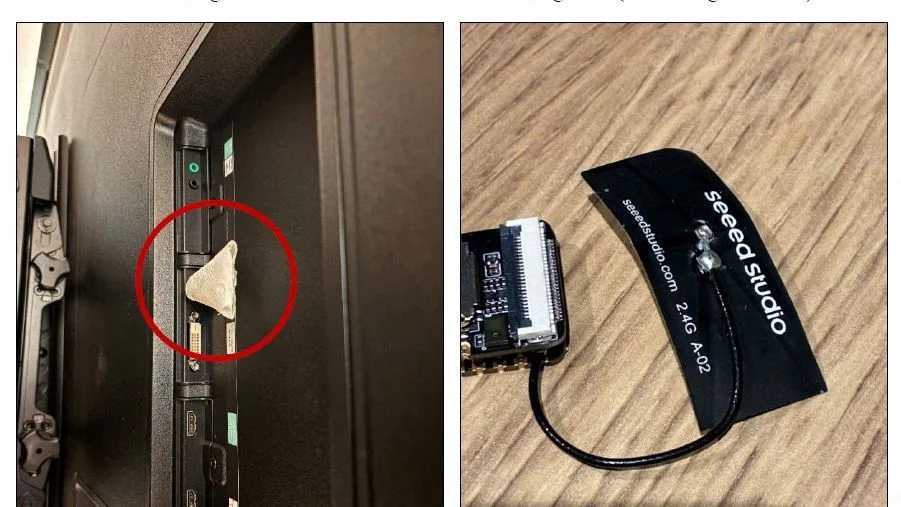
The incident, which surfaced following a report from the U.S. Department of Justice, involves a Saudi Arabian national identified only as "A." The suspect, who had been employed at the company since July 2025, stands accused of orchestrating a covert surveillance operation within the heart of OpenAI’s leadership offices. According to court filings, the engineer allegedly planted a sophisticated recording device inside a television’s USB port, camouflaged within a crumpled piece of toilet paper to evade detection.
The conference room in question was no ordinary office space; it served as a hub for the most sensitive deliberations within the organization. Investigators note that discussions within these walls routinely covered classified research breakthroughs, long-term product roadmaps, delicate business negotiations, and high-level communications with government regulators. The potential compromise of such information represents a nightmare scenario for a company whose valuation and competitive advantage are built almost entirely upon intellectual property and technical secrets.
Chronology of the Operation
The unraveling of the plot began on September 30, when the recording device was discovered during a routine security sweep. Forensic analysis of the incident suggests the following timeline of events:
- September 28: Investigators believe the suspect entered the conference room and installed the recording device. Although the engineer did not have explicit authorization to be in that specific area, surveillance footage captured him lingering near the room on multiple occasions.
- September 30: The device was discovered by staff. It was found plugged into the USB port of a television, carefully concealed.
- October 9: Federal authorities apprehended the suspect.
- October 15: The U.S. Department of Justice publicly announced the charges, including the unlawful interception of oral communications. The suspect appeared before a federal judge in San Francisco.
- October 19: A follow-up hearing is scheduled to determine the suspect’s detention status.
The sophistication of the attempt is underscored by the evidence gathered by the FBI. During a search of a bag the suspect had abandoned on company premises, agents uncovered a secondary device of a similar nature, suggesting a planned redundancy or a potential expansion of the surveillance efforts.
Supporting Data and Premeditation
Perhaps the most damning evidence against the accused lies in his digital footprint. Court documents reveal that an AI-assistant account linked to the suspect’s wife was used to conduct a series of highly suspicious queries. These queries, which occurred prior to the breach, sought detailed technical instructions on how to construct an audio recording device, methods for real-time remote monitoring, and advanced encryption techniques to transmit or store the stolen data.
The suspect’s background adds another layer of complexity to the investigation. Having held a permanent resident status in the United States since 2020, he was a veteran of the tech industry with a resume that reportedly included stints at industry titans such as Microsoft and Meta. This history suggests a deep familiarity with the security protocols typical of Silicon Valley’s largest firms, making his actions all the more deliberate in the eyes of federal prosecutors.
Official Responses and Internal Security Measures
OpenAI has moved quickly to distance itself from the individual and reassure its stakeholders. In a statement released shortly after the charges were made public, an OpenAI spokesperson confirmed that the company immediately terminated the engineer’s employment upon his arrest.
"The device was specifically engineered to be difficult to detect, indicating a high level of intent," the spokesperson noted. The company has been cooperating fully with the Federal Bureau of Investigation (FBI). Addressing the immediate concerns of investors and clients, the company stated: "Bislang haben wir keine Hinweise darauf, dass diese Person unberechtigt auf Modellparameter, Quellcode oder Kundendaten zugegriffen hat" (To date, we have no evidence that this individual accessed model parameters, source code, or customer data without authorization).
While the company’s assertion provides some solace, the mere fact that an internal actor was able to bypass physical security measures to monitor executive discussions has prompted an immediate audit of OpenAI’s internal security culture.
Legal Implications and Potential Penalties
The legal repercussions for the accused are severe. The charge of unauthorized interception of communication is a felony in the United States. If convicted, the suspect faces a maximum sentence of five years in federal prison and potential fines reaching up to $250,000.
The case is being treated with significant gravity by the Department of Justice, as it touches upon the broader national security implications of AI development. As AI becomes a critical component of infrastructure, the protection of the firms developing these technologies has moved from the realm of corporate policy to the realm of national interest.
The Broader Context: Security in the Age of AI
This incident highlights a burgeoning tension in Silicon Valley: the conflict between the open-source, collaborative culture that birthed AI and the intense, "bunker-mentality" security required to protect these powerful systems.
As noted in recent industry discourse—and highlighted by figures like Fields Medalist Peter Scholze—the speed at which AI models are advancing is creating an environment where humans are increasingly seen as the primary bottleneck or, in some cases, the primary security risk. When a single engineer can potentially threaten the core secrets of a multi-billion dollar entity, the traditional "trust-but-verify" model of corporate employment is clearly insufficient.
Furthermore, the incident raises questions about the "insider threat" model in the tech industry. With the mobility of talent between firms like Microsoft, Meta, and OpenAI, protecting proprietary knowledge is becoming an impossible task. The reliance on digital assistants to plan physical crimes, as alleged in this case, represents a meta-irony: the very technology OpenAI is developing to assist humanity was allegedly used to subvert its own security.
Looking Forward: A Paradigm Shift?
The aftermath of this scandal will likely force OpenAI and its peers to overhaul their physical and digital security architectures. We can expect to see:
- Increased Surveillance of Physical Assets: The era of "smart office" convenience, where televisions and peripheral devices are easily accessible, is likely coming to an end. Expect tighter controls on hardware and USB ports.
- Enhanced Vetting and Insider Threat Monitoring: Tech firms will likely shift toward more aggressive, AI-driven behavioral analysis of their own employees to identify patterns of disloyalty or suspicious intent long before they manifest in physical security breaches.
- The "Bunker" Strategy: As AI models grow more capable, the firms developing them may adopt security postures more akin to defense contractors or government intelligence agencies than traditional tech startups.
As the legal proceedings continue in San Francisco, the case against the former OpenAI engineer serves as a stark, cautionary tale. In the race to build the future, the most dangerous vulnerability may not be the code, the hardware, or the algorithms—but the individuals who walk through the front door with their own agendas. For OpenAI, the challenge is now to secure its future without stifling the very innovation that made it the most watched company in the world.