The global fashion retail landscape was rattled this week as British online retail giant ASOS became the latest high-profile victim of a significant cybersecurity breach. Thousands of customers worldwide reported receiving alarming, cryptic notifications directly to their mobile devices, signaling a sophisticated compromise of the company’s digital infrastructure. As the company scrambles to contain the fallout, the incident has ignited widespread concerns regarding data privacy, the security of third-party service providers, and the resilience of global e-commerce platforms.
1. The Incident: A Digital Wake-Up Call
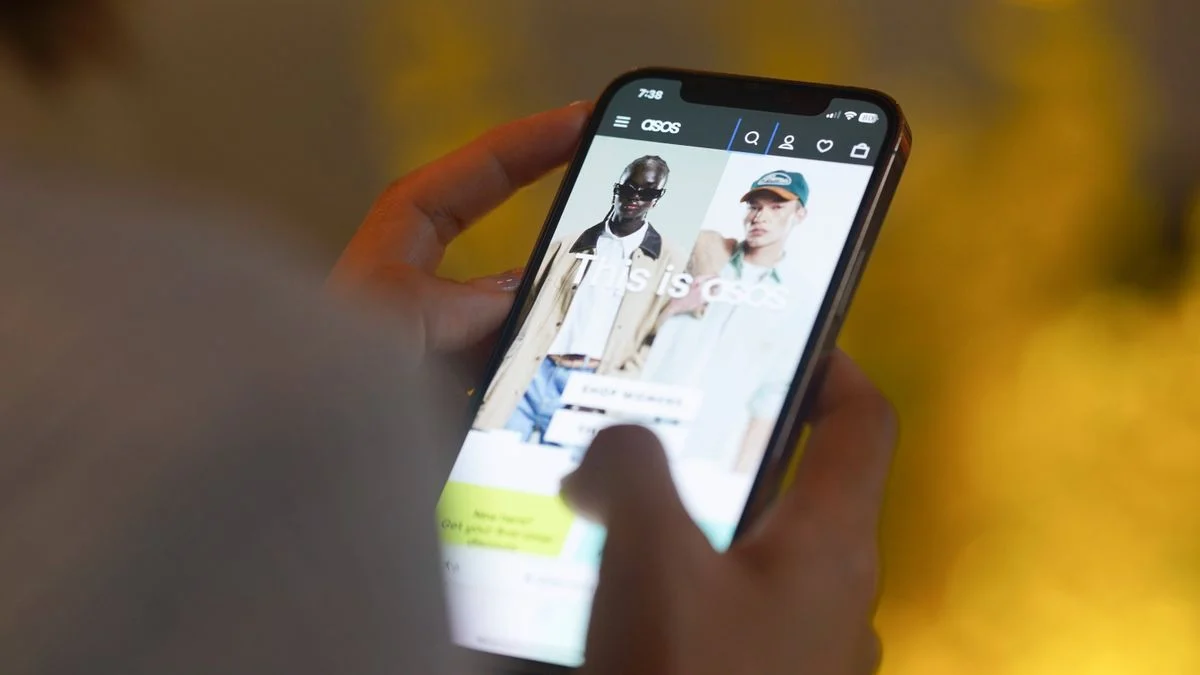
On Tuesday, the digital serenity of millions of ASOS shoppers was shattered by an unsettling push notification. Instead of the usual alerts regarding flash sales or new arrivals, users reported receiving a message with the blunt subject line: "ASOS Hacked."
The notification was not a routine system error; it was a targeted intrusion. Screenshots circulating rapidly across X (formerly Twitter) and Reddit revealed a chilling message directed at the company’s internal security teams. The perpetrators claimed to have fully compromised the "Snowflake instance" associated with the retailer—a critical cloud-based data storage and analytics platform used by many Fortune 500 companies to manage massive datasets.
The message left by the attackers was explicit: "Dear ASOS privacy and IT officers, we have fully compromised the Snowflake instance. Get in touch, otherwise we will publish it."
This intrusion marks a significant escalation in cyber threats against fashion retailers, which hold vast amounts of consumer behavioral data, contact information, and purchase histories. For ASOS, a company with approximately 17 million active customers globally, the breach represents a major reputational and operational challenge.
2. Chronology of the Breach
The unfolding of the event followed a rapid, high-pressure timeline that kept the retail and cybersecurity sectors on high alert throughout Tuesday.
- Early Tuesday Morning: Customers begin reporting the receipt of the "ASOS Hacked" push notifications. Social media platforms quickly fill with screenshots, sparking panic among the brand’s vast user base.
- Mid-Morning: The stock market reacts sharply to the news. ASOS shares plummet by more than 10% in early trading as investors digest the implications of a data breach involving such a large customer demographic.
- Afternoon: ASOS issues an official statement via its Instagram Stories, acknowledging "unauthorized customer notifications." The company confirms it is investigating the incident but attempts to soothe public concern by limiting the scope of the potential data exposure.
- Late Afternoon: Further reports emerge via the news agency PA, shedding light on the specific nature of the threat—specifically the mention of the "Snowflake" platform, which points to a potential supply-chain style attack rather than a direct breach of the main ASOS website.
3. The Snowflake Connection and Data Security
The inclusion of "Snowflake" in the attackers’ ransom note is a pivotal detail. Snowflake is a cloud-based data platform that allows companies to store, integrate, and analyze vast quantities of data. It is a backbone for modern enterprise analytics.
When an attacker claims to have "compromised an instance," they are suggesting that they have gained unauthorized access to the client’s specific data silo within that cloud environment. This is a common vector in modern cyberattacks: rather than attacking a well-defended, proprietary website, hackers target the third-party providers that store the company’s data.
ASOS has stated that its primary website and retail operations remain fully functional, suggesting the breach did not paralyze the company’s storefront. However, the compromise of a third-party communication platform suggests that the hackers managed to hijack the API or dashboard used to send push notifications to customers. This indicates a deep-seated security failure that allowed the attackers to manipulate official communication channels to broadcast their ransom demands.
4. Official Responses: Damage Control and Assessment
ASOS has adopted a cautious approach to communication, balancing the need for transparency with the need to avoid further inciting panic. In its official statement, the company addressed the most pressing fears of its user base:
- Scope of Data Exposure: The company confirmed that basic personal information, including names and contact details, may have been accessed. This type of data is the "bread and butter" for phishing campaigns and social engineering, making customers vulnerable to future scam attempts.
- Financial Security: Crucially, ASOS explicitly stated: "We do not believe that payment card information or account passwords were affected." This is a significant relief, as payment data theft would trigger stringent regulatory fines under GDPR and other international privacy laws, potentially costing the company tens of millions of dollars.
- Operational Status: The retailer emphasized that it is not experiencing any service interruptions. The storefronts for ASOS, as well as its sub-brands like Topshop and Miss Selfridge, remain online and are currently processing orders as normal.
"We are currently investigating unauthorized activities on third-party platforms that we use for communicating with customers," the company noted, reinforcing the narrative that the breach was external to their core proprietary systems.
5. Implications for the Retail Industry
The ASOS breach serves as a case study for the vulnerabilities inherent in the modern, hyper-connected digital retail ecosystem.
The Rise of Supply-Chain Attacks
As retailers move their data to cloud platforms like Snowflake and rely on dozens of third-party apps for marketing, customer support, and logistics, their attack surface grows exponentially. Each third-party integration is a potential "backdoor." If a marketing tool or a data analytics plugin is compromised, the attacker can leverage that trust to access the parent company’s ecosystem.
The Impact on Consumer Trust
For a brand like ASOS, which relies on a demographic of young, digital-native shoppers, trust is the currency of the business. An incident where customers receive a "Hacked" notification on their phones undermines the brand’s image of digital competence. The immediate 10% stock drop reflects investor fear that customer churn could follow if consumers lose confidence in the brand’s ability to protect their identity.
Regulatory Scrutiny
Given that ASOS operates in the UK and internationally, it is subject to the General Data Protection Regulation (GDPR) and the UK GDPR. These regulations require companies to inform data protection authorities of breaches that risk the rights and freedoms of individuals. The ICO (Information Commissioner’s Office) will likely launch an inquiry to determine if ASOS exercised "reasonable care" in protecting its third-party data environments.
6. What Should Customers Do?
While ASOS has stated that financial information appears secure, cybersecurity experts urge customers to remain vigilant. The data potentially leaked—names and contact details—is often used to facilitate "spear-phishing."
- Be Wary of Emails: Attackers who have names and email addresses can craft highly convincing emails that appear to come from ASOS. If an email asks for a password reset or for payment details to be "re-verified," it is likely a scam.
- Monitor Accounts: Even if passwords weren’t stolen, it is good security hygiene to change your ASOS password immediately, especially if that same password is used on other sites.
- Enable MFA: If ASOS offers Multi-Factor Authentication, users should enable it immediately.
- Watch for "Social Engineering": If you receive phone calls or SMS messages from someone claiming to be from ASOS support, verify the caller’s identity through official channels before sharing any information.
7. Conclusion: The Path Forward
The situation remains fluid. As of this report, ASOS continues to work with cybersecurity forensic experts to "harden" their systems and close the loopholes that allowed the attackers to seize control of their notification infrastructure.
The broader lesson for the retail sector is clear: digital transformation without robust, end-to-end security—including the vetting of every third-party service—is a liability. As the investigation progresses, the tech community will be watching closely to see how the "Snowflake" vulnerability was exploited. For ASOS, the task ahead is twofold: they must restore their reputation among a global customer base of 17 million people, and they must demonstrate to regulators that they have the systems in place to prevent a recurrence of this digital intrusion.
While the immediate threat to customer finances appears to have been mitigated, the psychological impact of the breach on the company’s brand equity may take much longer to repair. In an era where data is the most valuable commodity, the "ASOS Hacked" notification serves as a blunt reminder that for modern retailers, the digital storefront is only as strong as the weakest link in their cloud architecture.