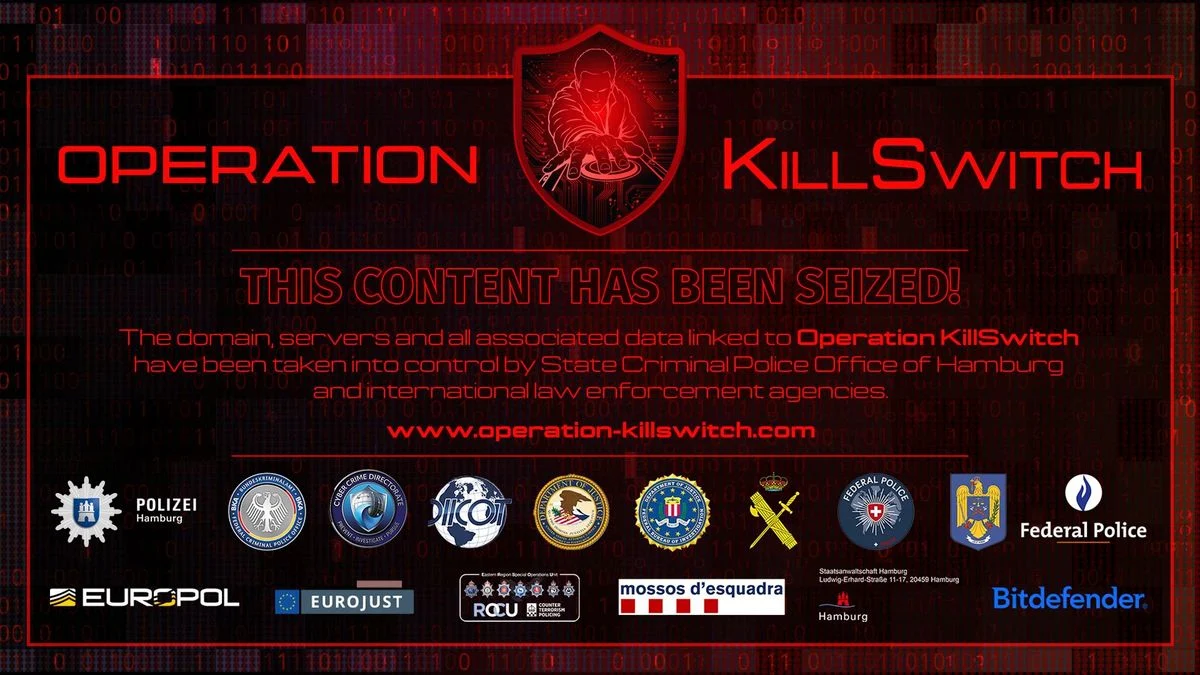
In a striking revelation that has sent shockwaves through the global cybersecurity community, German authorities have announced the successful neutralization of "KillSec," a sophisticated cybercrime collective responsible for a string of high-profile data extortion attacks. What makes the case particularly alarming to security analysts is the age of the primary actors: the alleged mastermind behind the operation is a mere 16-year-old, supported by a core team of minors and young adults who leveraged cutting-edge artificial intelligence to extort organizations worldwide.
The crackdown, codenamed "Operation Killswitch," represents a significant victory for the Hamburg State Criminal Police (Landeskriminalamt) and international law enforcement agencies, marking a paradigm shift in how authorities approach the increasingly youthful demographic of high-level cybercriminals.
Main Facts: The Rise and Fall of KillSec
Since its inception in 2024, the KillSec group operated with a ruthless, business-like efficiency. Their modus operandi was straightforward yet devastating: infiltrate the networks of organizations, exfiltrate vast quantities of sensitive data, and threaten to publish the information on a public "leak site" unless a substantial ransom was paid.
According to reports released by Hamburg police, the group was linked to approximately 1,000 separate cyberattacks globally, with 70 confirmed incidents occurring within Germany alone. The group did not merely function as a loose collection of hackers; they operated with a defined corporate-like hierarchy. The 16-year-old lead operator sat at the helm, while a 17-year-old associate managed core technical operations. Furthermore, the group utilized specialized roles, including dedicated negotiators who handled ransom demands and "distribution partners" tasked with marketing the stolen data on the dark web.
The scale of the breach is staggering. Investigators successfully seized control of the group’s infrastructure, preventing the imminent release of 110 terabytes of sensitive, stolen data. This cache, had it been leaked, would have likely caused irreparable damage to hundreds of private firms, government agencies, and individual victims.
Chronology of the Investigation
The investigation, which began in early 2025, moved at a pace seldom seen in complex digital crimes. The rapid escalation of KillSec’s activity—coupled with their increasing audacity—triggered a multi-jurisdictional response.
- Early 2025: Hamburg authorities, following a trail of digital footprints linked to extortion payments, officially launched a concentrated investigation into the KillSec entity.
- Spring 2025: Collaboration between the Hamburg State Criminal Police and international partners across eight European countries and the United States intensified. Intelligence sharing allowed authorities to map the group’s infrastructure, which was geographically dispersed across multiple continents.
- The Operational Phase: The culmination of the investigation involved a synchronized series of raids. Police executed search warrants at eight distinct locations in Greece, Romania, Spain, and the United Kingdom. These raids were not merely arrests; they were forensic goldmines. Authorities secured servers, high-end workstations, financial records, and evidence of the digital wallets used to launder cryptocurrency ransom payments.
- The Takedown: In a final, decisive move, the Hamburg investigators assumed control of the KillSec leak site. By replacing the site’s content with a law enforcement seizure notice, the police effectively cut off the group’s primary avenue for extortion and communication, halting ongoing blackmail attempts in their tracks.
Supporting Data: AI-Powered Extortion
One of the most concerning aspects of the KillSec operation was the group’s early adoption and integration of Artificial Intelligence (AI). While many cybercriminals still rely on manual vulnerability scanning, KillSec utilized AI models to automate the reconnaissance phase of their attacks.
The group deployed specialized algorithms to identify potential victims, assess the value of their data, and even draft personalized extortion emails designed to maximize the likelihood of payment. By automating the "sales funnel" of cybercrime, the 16-year-old and his team were able to maintain a high tempo of operations that overwhelmed traditional corporate defenses.
The data seized during the raids—totaling 110 terabytes—included internal business documents, employee records, and, in some cases, highly sensitive personal information of private citizens. This volume of data underscores the sheer scope of the threat. Had this information been dumped into the public domain, it would have created a secondary wave of identity theft and corporate espionage that could have lasted for years.
Official Responses and Strategic Significance
The operation has been hailed as a landmark success by German officials. Hamburg’s Interior Senator, Andy Grote (SPD), underscored the gravity of the situation during a press conference on Thursday.
"After ‘Operation Medusa,’ which targeted the distribution of illicit imagery, the international strike against the ‘KillSec’ group is already the second major international operation within a few months in which the Hamburg State Criminal Police has played a leading role," Grote stated. He emphasized that the successful apprehension of these individuals serves as a stern warning to others who believe they can hide behind the "facade of anonymity" provided by the internet.
The international cooperation was unprecedented. Law enforcement agencies from across Europe and the United States worked in real-time, synchronizing raids across different time zones to ensure that evidence was not wiped remotely by the suspects. This level of cross-border synergy is increasingly necessary, as cybercrime groups have evolved to treat national borders as irrelevant to their operations.
Implications: The New Frontier of Juvenile Cybercrime
The fact that the alleged ringleader was only 16 years old at the time of the arrest highlights a disturbing trend in modern criminal sociology: the "gamification" of cybercrime. For the current generation of digitally native youths, the technical barriers to entry for sophisticated cybercrime have been lowered by the availability of "Ransomware-as-a-Service" (RaaS) models and AI-assisted tooling.
The Human Cost
Beyond the technical data, the human impact of these attacks is profound. When a company or government entity is hacked, the victims are not just the organizations themselves, but the citizens whose data is exposed. Recent incidents, such as the major cyberattack on the Berlin city administration, have shown that when public services are paralyzed by ransomware, the ripple effects—from delayed medical appointments to bureaucratic gridlock—can cause significant suffering.
Preventive Measures
As the dust settles on Operation KillSec, experts are urging organizations to take proactive measures to mitigate the risks of such attacks. Key recommendations include:
- Zero-Trust Architecture: Assuming that any network connection could be compromised and limiting access accordingly.
- Robust Data Backups: Ensuring that critical data is backed up in an offline, immutable state, rendering ransom demands moot.
- Employee Training: Educating staff on the nuances of social engineering, which remains a primary entry point for even the most sophisticated hacking groups.
The Road Ahead
The case of KillSec will undoubtedly be studied for years to come. It raises uncomfortable questions about how education systems and social services can better engage with tech-savvy youth before they transition from curiosity to criminality. Furthermore, it challenges law enforcement to keep pace with an adversary that is not only younger and more tech-literate but also increasingly comfortable using the very tools—AI—that are designed to protect society.
As the legal proceedings begin in Germany, the global cybersecurity community watches closely. The prosecution of these individuals will set a precedent for how juvenile offenders are treated in cases of transnational, high-stakes cyber terrorism. For now, however, the digital locks have been changed, the leak sites are offline, and one of the most prolific teenage cyber-syndicates has been effectively silenced.
The success of Operation Killswitch is a reminder that while the digital world offers near-infinite connectivity, it also provides a global stage for those who wish to do harm. It is a testament to the fact that, eventually, even the most "anonymous" actors leave a trail that leads back to the physical world—and into the hands of the law.