In a proactive response to a severe cybersecurity threat, a vast array of public authorities and institutions across the German state of Hesse were forced to take their digital infrastructure offline this week. The preemptive move, designed to shield sensitive data from potential exploitation, affected everything from state government portals to high-security federal agencies and municipal service websites.
The disruption, which began on Wednesday, served as a stark reminder of the fragile interconnectedness of modern digital infrastructure. As the global cybersecurity community scrambled to address a critical flaw in the PHP programming language—a cornerstone of the modern web—the state of Hesse opted for a "better safe than sorry" approach, prioritizing data integrity over constant accessibility.
The Scope of the Disruption
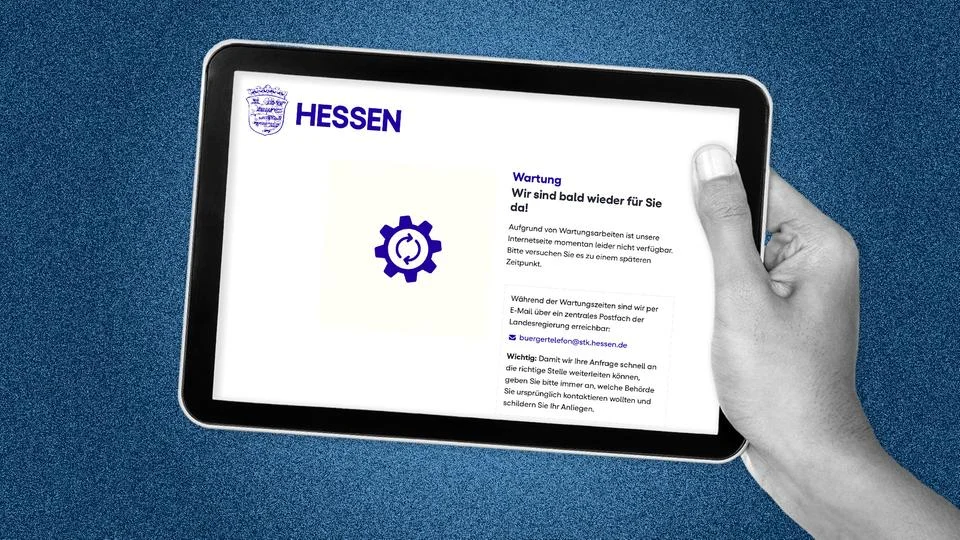
The digital blackout was widespread, affecting entities that form the backbone of public administration in the region. Visitors to the official Hesse state portal, hessen.de, were greeted not by the usual array of government services, but by a stark maintenance page: "Due to maintenance work, our website is unfortunately unavailable. Please try again at a later time."
The list of affected institutions was extensive, illustrating the ubiquity of the compromised technology. Key entities forced offline included:
- The Hesse State Government: Including all ministry portals and subordinated authorities.
- Federal Law Enforcement: The Federal Criminal Police Office (BKA) in Wiesbaden.
- Municipalities: The cities of Kassel, Wiesbaden, and Offenbach.
- Academic Institutions: The University of Kassel and the Frankfurt University of Applied Sciences.
- Public Health and Infrastructure: The university clinics of Gießen-Marburg and Frankfurt, as well as the Hesse Fire Department and various regional tourism portals like edersee.com.
By Wednesday evening, the majority of these services had begun the process of coming back online, following the implementation of emergency security patches.
Chronology of the Crisis
The situation unfolded rapidly as reports of the vulnerability moved from internal security circles to the public sphere.
- Tuesday: Security researchers identified two critical vulnerabilities within the PHP programming language. While a coordinated disclosure was planned to allow for the development of patches, technical details began to leak into the wild, heightening the risk of exploitation.
- Wednesday Morning: The Federal Office for Information Security (BSI) issued an urgent warning, classifying the risk level as "3/Orange." This classification indicates an "extraordinarily high" threat potential.
- Wednesday Midday: In response to the BSI warning, the Hesse state government and other institutions began a coordinated, precautionary shutdown of their web servers.
- Wednesday Afternoon: Developers of the PHP language officially released security updates to mitigate the flaw.
- Wednesday Evening: As system administrators applied the patches, institutional websites began the gradual process of restoring public access.
Understanding the Vulnerability: A Technical Overview
The crisis stems from a newly discovered set of vulnerabilities in PHP, a server-side scripting language that powers a massive percentage of the internet. From popular content management systems like WordPress and Drupal to complex, custom-built enterprise applications, PHP is the engine room of the digital world.
Dennis Kenji-Kipker, an IT security expert at the cyberintelligence.institute in Frankfurt, describes the flaw as exceptionally dangerous. "Two severe errors were discovered in PHP itself," Kipker explained. "Attackers can exploit these vulnerabilities remotely to execute malicious code on affected servers. They do not even need to authenticate—this is the level of severity we are dealing with."
In a successful exploit scenario, an attacker could gain unauthorized control over a server. This grants them the ability to access, exfiltrate, or delete sensitive data, including user databases, administrative credentials, and passwords. Because the vulnerability allows for Remote Code Execution (RCE), the potential for a complete system compromise is high.
Official Responses and Strategic Decisions
The decision to pull the plug on public-facing infrastructure is never taken lightly, particularly when it impacts the ability of citizens to interact with government services. However, both state and federal officials underscored the necessity of the action.
A spokesperson for the Hesse State Chancellery clarified that the move was purely prophylactic. "The temporary shutdown was carried out purely as a precaution to counteract potential security risks and to ensure the safety of our web services," the spokesperson stated, emphasizing that there was no evidence of an actual, successful hacker attack against the state’s systems prior to the shutdown.
The BSI’s involvement was instrumental in the decision-making process. By issuing the "Orange" alert, the agency provided a clear mandate for state-level IT departments to prioritize isolation over availability. This strategic caution is a hallmark of modern cybersecurity defense: isolating a system to prevent a breach is significantly cheaper and more efficient than remediating a full-scale ransomware or data theft incident after the fact.
Implications for Global Web Security
While the state of Hesse managed the situation with relative efficiency, the incident highlights a persistent systemic weakness. PHP is so deeply integrated into the global internet architecture that a single vulnerability can trigger a ripple effect across borders and sectors.
"This is not just a local issue; it is a global one," Kipker noted. "The fact that details leaked before a patch was widely deployed gave attackers a head start."
The incident also raises questions about the "dependency chain" in software development. Many public sector websites rely on third-party frameworks and plugins that run on PHP. Even if a government agency updates its own code, the underlying language or the CMS (like Joomla! or TYPO3) may remain vulnerable until a patch is propagated through the entire stack.
Recommendations for Web Administrators and Users
For those managing web infrastructure, the events of this week serve as a critical wake-up call. Security experts recommend a multi-tiered approach to hardening systems:
- Immediate Patching: Administrators must prioritize the installation of the official PHP security updates released by the language’s maintainers.
- Audit Legacy Systems: Older, "End-of-Life" versions of PHP that no longer receive official support represent a critical liability. These systems should either be upgraded or isolated behind advanced firewall protections (WAFs).
- Incident Response Planning: The swift coordination in Hesse demonstrates the value of pre-existing communication channels between the BSI and state-level IT departments.
For the general public, the implications are more nuanced. As the BSI clarified, there is no direct risk to the average user’s smartphone or PC, as the vulnerability resides on the server-side, not the client-side. However, the secondary effects—service outages and the potential risk of data exposure if a server was compromised before the patch—remain a concern. Users are advised to monitor official communications from institutions they interact with and, as a matter of best practice, update their passwords for any government or financial portals that may have been affected.
Conclusion: The Cost of Vigilance
The events in Hesse underscore the reality of the "new normal" in digital governance. As cyber threats become more sophisticated and vulnerabilities more systemic, the ability to rapidly deploy defensive measures—even at the cost of temporary, high-profile downtime—is becoming a vital component of public service.
While the "maintenance" messages on Hesse’s websites may have caused minor inconvenience to citizens, they represented a successful exercise in collective defense. By acting before an exploit could be realized, the state successfully mitigated a threat that, had it been ignored, could have resulted in significant data breaches or the long-term degradation of public trust in digital infrastructure.
As the digital landscape continues to evolve, the partnership between security agencies like the BSI and local institutions will remain the primary defense against the ever-present threat of those seeking to exploit the invisible vulnerabilities upon which our modern lives are built. The crisis has been averted for now, but the episode serves as a persistent reminder: in the digital age, security is not a static state, but a continuous, active, and often disruptive process.