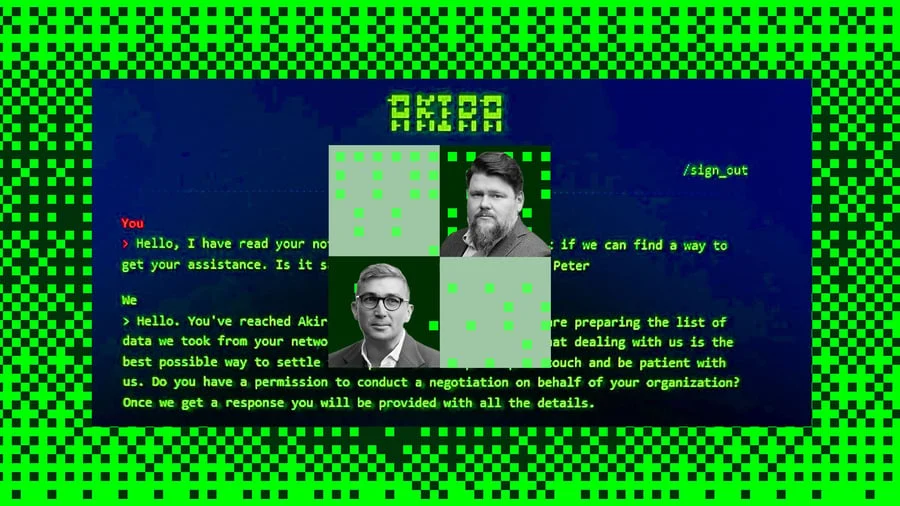
In an era where digital infrastructure is the lifeblood of global commerce, the specter of ransomware has evolved from a nuisance into a systemic threat. Cyber-attacks are no longer confined to the technology sector; they are increasingly paralyzing industrial production, supply chains, and administrative functions across the board. For the modern medium-sized enterprise, or "Mittelstand," the question is no longer if an attack will occur, but how the organization will survive the aftermath.
As organizations grapple with the reality of encrypted servers and extortionate demands—often paid in untraceable Bitcoin—the need for a strategic, crisis-hardened response has never been greater. Experts Michael Sjåberg and Peter Skovbo, founders of the Swiss-based consultancy Delta Crisis, argue that a ransomware incident is a total corporate emergency, not merely an IT glitch.

The Anatomy of a Ransomware Crisis: Main Facts
Ransomware is a malicious software variant that encrypts a victim’s files, effectively holding their digital assets hostage. The attackers, typically sophisticated criminal syndicates, demand payment for the decryption key. However, the modern playbook has shifted: attackers now frequently employ "double extortion." This involves exfiltrating sensitive company data before encryption, threatening to leak trade secrets, employee records, or client data on the dark web if the ransom is not met.
The core challenge for management is the speed at which the crisis unfolds. Within hours, entire production lines can grind to a halt, financial reporting can be compromised, and the reputation of the firm can be irreparably damaged.

Chronology of a Catastrophe: The First 48 Hours
When a company realizes it has been compromised, the following timeline is typical of the chaos that ensues:
Hour 0–4: Detection and Triage
The incident is usually flagged by an automated security alert or by employees reporting "file not found" errors or locked systems. The immediate reaction is often panic. IT departments scramble to disconnect systems from the network, which—while necessary to prevent lateral movement—often destroys volatile forensic evidence needed to identify the entry point.
Hour 4–12: Containment and Assessment
Management must establish a "War Room." This group should include the CEO, legal counsel, PR, and specialized cyber-incident response experts. The primary goal is to determine the scope: What is encrypted? What was stolen? Is the backup infrastructure safe?
Hour 12–24: The Negotiation Dilemma
This is the most critical juncture. Should the company engage with the hackers? Experts like Sjåberg emphasize that negotiation is not about paying; it is about buying time. The goal is to stall the attackers, gather information about the threat actor, and assess the feasibility of recovery without payment.

Hour 24–48: Strategic Decision Making
By this point, the business impact assessment must be finalized. Leadership must weigh the cost of downtime against the risks of paying a ransom, which provides no guarantee that data will be returned or kept private.
Supporting Data: Why the Mittelstand is the Prime Target
Cybercriminals have pivoted toward the mid-market because these firms often possess the wealth to pay significant ransoms but lack the robust, enterprise-grade cybersecurity budgets of multinational corporations.
- The Proliferation of Ransomware-as-a-Service (RaaS): The barrier to entry for criminals has vanished. Sophisticated malware is now rented out on the dark web, allowing even low-skill attackers to execute high-impact strikes.
- Production Downtime Costs: For a manufacturing company, the cost of an hour of lost production can range from tens of thousands to millions of dollars. This makes the "willingness to pay" significantly higher than the actual ransom demand.
- Data Leakage Risks: The threat of GDPR violations and regulatory fines following a data breach often forces companies to prioritize privacy over security, leading them to pay just to prevent the public disclosure of sensitive information.
Expert Perspectives: Lessons from the Field
Michael Sjåberg, who draws on his background in military hostage negotiation, views a ransomware attack through the lens of human psychology. "Cybercrime is never just a technical issue," he notes. "It is an organizational one. When the systems go dark, the pressure on the CEO is equivalent to that of a hostage crisis. The decisions made in those early hours dictate the outcome."
Peter Skovbo adds that many companies fail because they treat IT security as a cost center rather than a strategic asset. "Companies invest in firewalls but neglect the human element—the training, the protocols, and the crisis communication plans," Skovbo explains. "When the attack hits, if you don’t know who is authorized to make a decision, you lose."

Official Responses and Regulatory Implications
Governments and law enforcement agencies globally are increasingly discouraging ransom payments. The argument is simple: payment fuels the criminal economy and incentivizes further attacks. However, the legal landscape is complex.
In many jurisdictions, companies are legally obligated to report data breaches to authorities within a specific timeframe (e.g., 72 hours under GDPR). Failure to do so can lead to massive fines. Furthermore, there is the risk of violating anti-money laundering (AML) laws if a ransom is paid to an entity currently under government sanctions.
Recommended Defensive Protocols
- Immutable Backups: Ensure backups are air-gapped or stored in a way that they cannot be encrypted or deleted by the malware.
- Zero Trust Architecture: Assume the network is already compromised. Limit access permissions so that if one account is breached, the attacker cannot move across the entire system.
- Crisis Simulation: Conduct "tabletop exercises" where executives walk through the steps of a simulated attack. Muscle memory is the best defense against panic.
Implications: The Long Road to Resilience
The aftermath of a ransomware attack is a grueling period of remediation. Beyond the immediate technical recovery, companies must navigate the legal fallout, potential class-action lawsuits from customers, and the long-term erosion of trust with partners and stakeholders.
The Shift Toward Resilience
The most resilient companies are those that have accepted "cyber-resilience" as a core business principle. This means building systems that can operate in a degraded state and having a pre-negotiated retainer with incident response firms.
Conclusion
Ransomware is the defining corporate challenge of the digital age. It tests the limits of leadership, technical capability, and ethical decision-making. As Sjåberg and Skovbo remind us, the goal is not to be invincible—because no system is—but to be prepared. When the screen goes black, the companies that survive are those that have already decided how they will fight back, how they will communicate with their stakeholders, and how they will ensure the continuity of their business under the most extreme pressure.
As we look toward the future, the integration of AI in both launching and defending against attacks will accelerate the pace of this digital arms race. Organizations that remain static in their defense strategies are, by definition, falling behind. The time to harden the perimeter, refine the internal culture, and prepare for the inevitable is today—before the ransom note appears.